
PanGuard AI
A self-hosted AI agent security tool that scans skills and MCP servers and guards tool calls offline, with no account required.
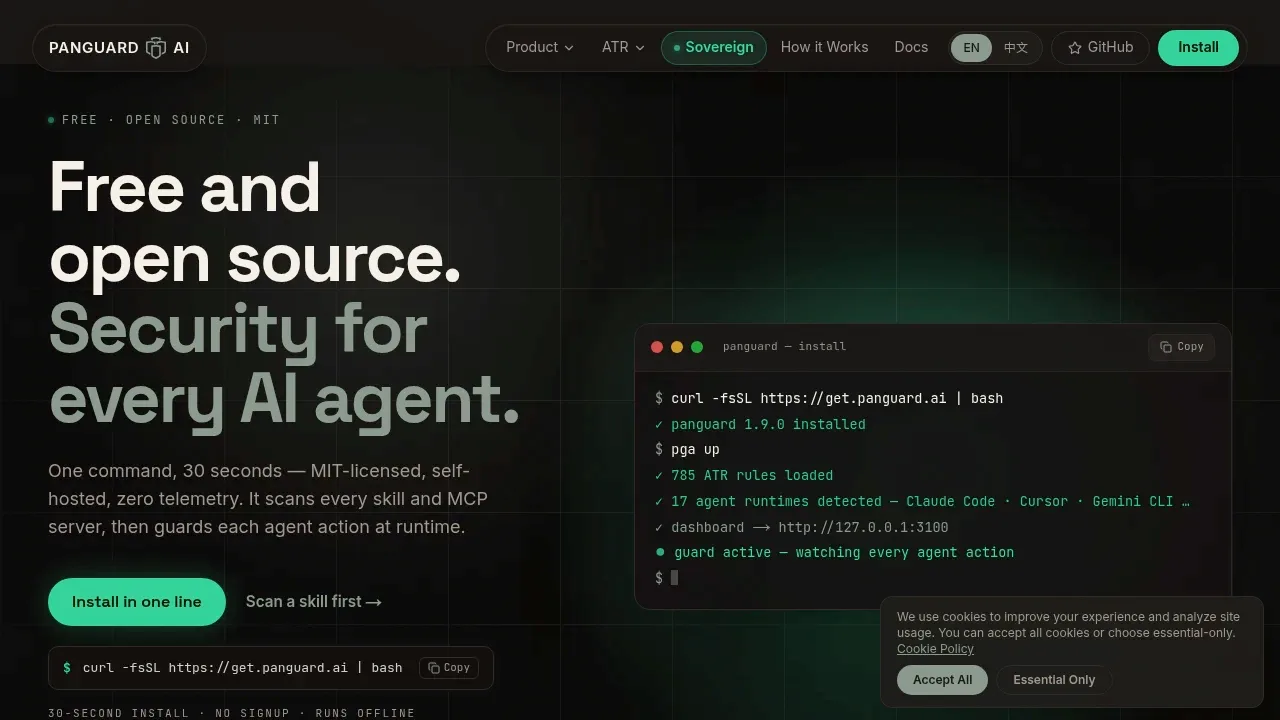
PanGuard AI checks skills and MCP servers for threats before AI agents load them, then watches their actions at runtime. It's for developers and teams who want protection against prompt injection, poisoned tools and malicious skills.
- Skill audits: Scan skills and MCP servers before use, with SARIF reports that teams can use to reject threats in CI.
- Runtime protection: Inspect MCP calls and built-in agent tools, including shell commands, file edits and web requests, and block known attacks using local ATR rules and heuristics.
- Agent integrations: Protect agents in Claude Code, Cursor, Codex CLI, Gemini CLI, Cline and other supported environments.
- Local dashboard: Check protection status, inspect findings and quarantine threats, with matched rules explaining detections.
- Optional AI review: Use Ollama locally or a cloud provider for a second opinion that flags findings for review rather than blocking actions itself.
The free, self-hosted runtime is open source under the MIT license. Rule-based detection and heuristics run on your machine and work offline without an account or a configured language model.
AI review and collective threat sharing are off by default. Cloud AI review sends requests to the chosen provider. If you enable sharing, the hosted Threat Cloud receives limited threat signatures, excluding prompts, code, file contents, paths and secrets.


