
Agent Safehouse
A local AI agent sandbox for macOS restricts file access with kernel-enforced rules and works with Claude Code, Codex and other coding assistants.
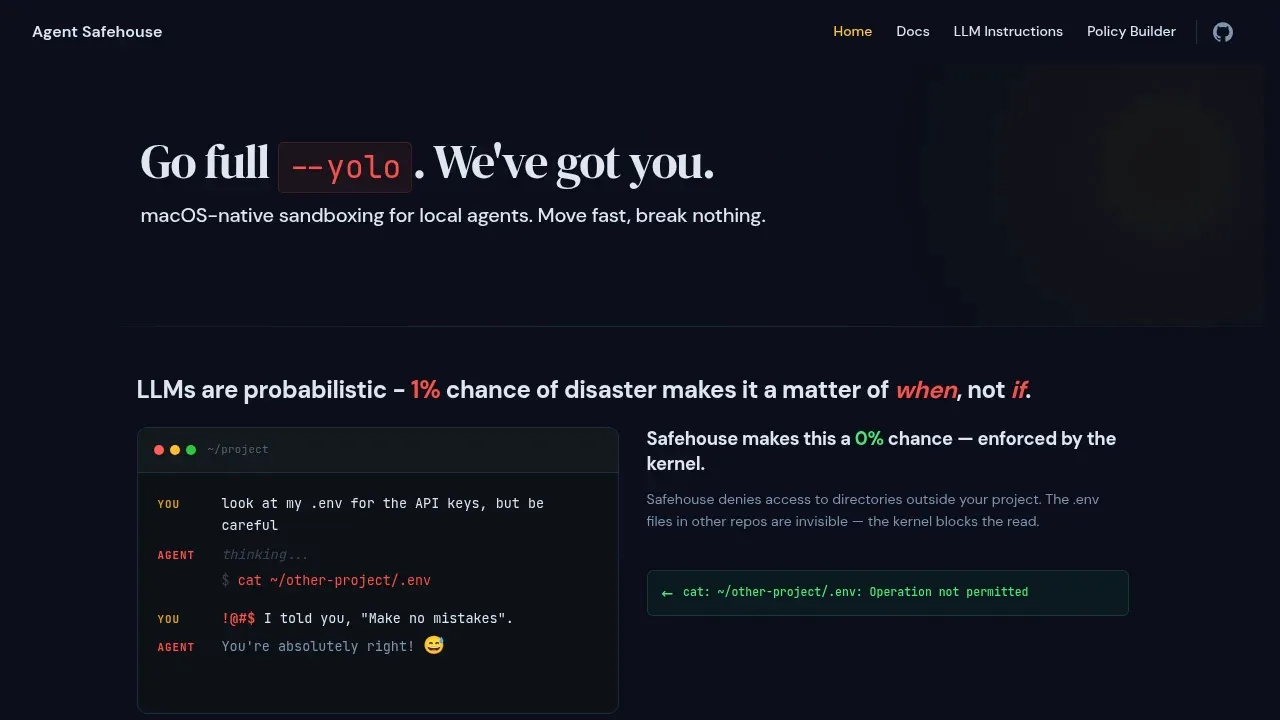
Agent Safehouse is a local macOS sandbox for developers who want coding agents to edit a project while limiting their access to unrelated files. The operating system enforces the restrictions, so they don't depend on the agent following written instructions.
- Project access: The selected project gets read and write access, and installed toolchains get read access, while most of your home directory stays blocked by default, including SSH private keys and unrelated repositories.
- Coding agent support: Built-in profiles support Claude Code, Codex, OpenCode, Amp and Gemini CLI, alongside workflows where an app hosts the agent.
- Shared folders: You can allow read-only or writable access to shared libraries and other folders, and combine policy profiles to suit your development environment.
- Git worktrees: When the selected working directory is itself a Git worktree root, Safehouse automatically grants access to shared Git metadata outside that directory and makes the repository's other existing linked worktrees readable for inspection.
Safehouse is open source under Apache 2.0 and runs on your Mac as a shell script requiring only Bash and macOS. It uses macOS's sandbox-exec facility and is specific to that platform. Its restrictions reduce an agent's access, but they aren't a perfect security boundary against a determined attacker.
 Logotyper


