
Nox
A local security scanner for AI apps and MCP servers that checks prompt injection and agent permissions, with offline analysis under Apache 2.0.
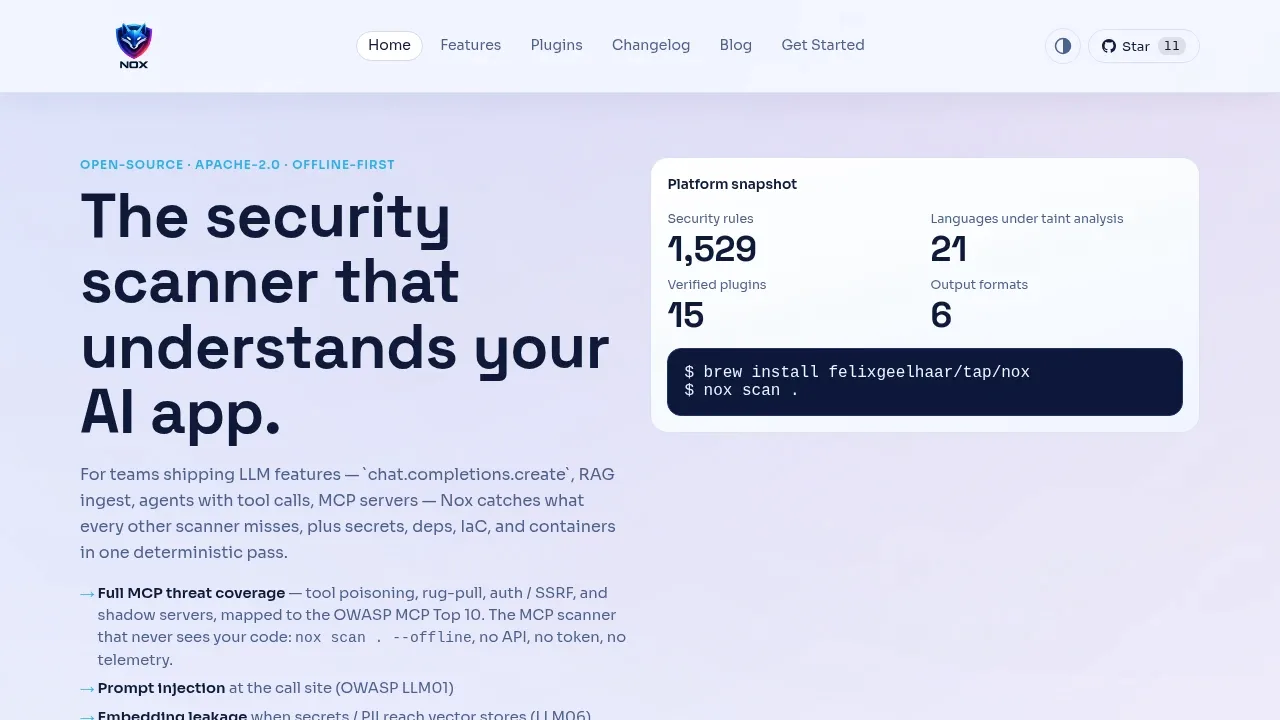
Nox is a security scanner for developers building LLM applications, RAG systems and agents with tool access. It traces untrusted input into model calls and model output into dangerous operations, including paths across functions and files.
- AI and agent checks: Detect prompt-injection risks, secrets or personal data entering vector stores, excessive agent permissions and unsafe coding-agent configuration.
- MCP security: Check for tool poisoning, malicious tool changes, authentication weaknesses, unsafe requests and shadow servers.
- Application security: Scan for credentials, infrastructure misconfiguration and dependency vulnerabilities, alongside dataflow risks such as SQL injection and path traversal.
- Supply-chain checks: Flag undeclared package imports that may reflect hallucinated packages and code that repeats known vulnerability patterns without an advisory lookup.
- Reports and agent access: Export SARIF for GitHub Code Scanning, CycloneDX and SPDX inventories, HTML reports and an AI component inventory; a built-in MCP server gives agents read-only access to results within allowed workspaces.
Nox is free and open source under Apache 2.0. Core analysis runs locally offline without an API token or telemetry. Dependency advisory lookups require network access, and Nox reports failed lookups or plugins as coverage gaps.
Optional LLM plugins send findings and code snippets to a configured endpoint, with Ollama among the supported providers. The optional adversarial-evaluation plugin sends attack prompts to a model endpoint. Official plugins have Cosign signatures verified through Sigstore.
 Logotyper


