
open·kritt
A self-hosted AI security research tool that scans local or remote code repositories, validates potential vulnerabilities, and ranks findings by custom severity
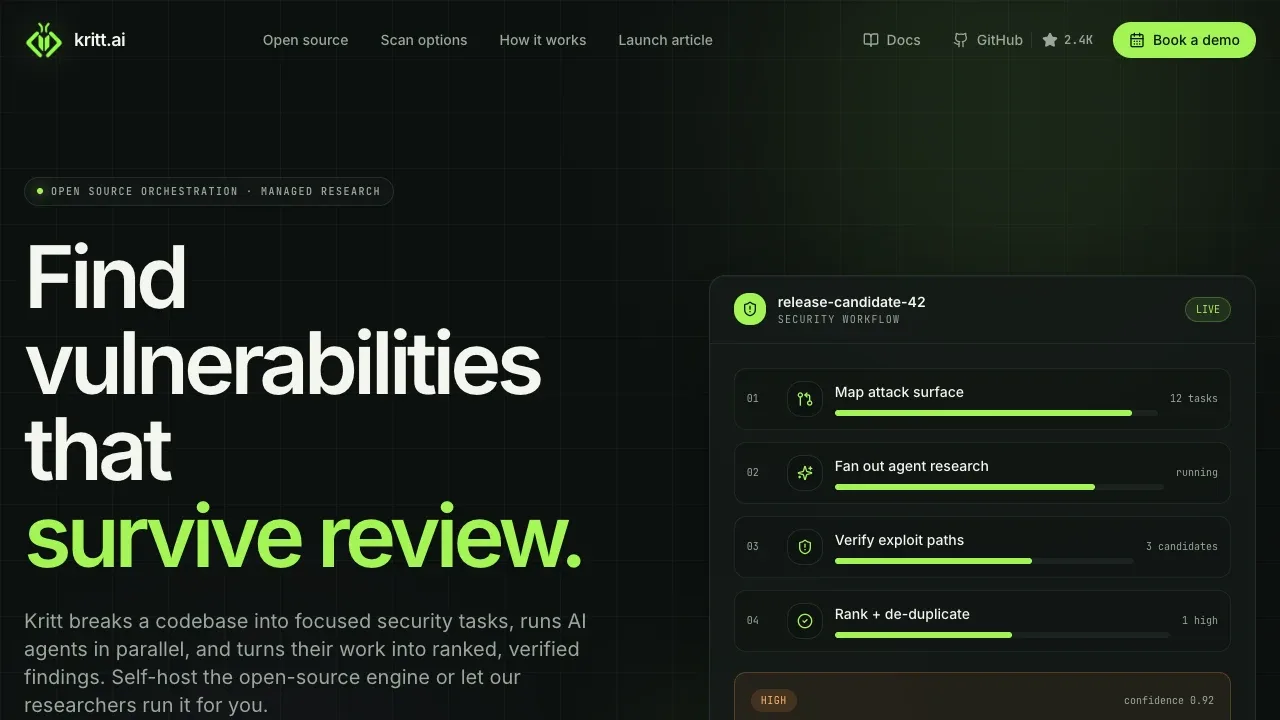
open·kritt helps security researchers and developers investigate code for vulnerabilities through focused AI agent tasks. It gives teams control over the research prompts, workflows, model providers, and infrastructure they use to review a codebase.
- Focused research workflows: Build reusable sequences of security prompts and run agents in parallel across files, functions, and attack hypotheses.
- Repository analysis: Scan local or remote repositories and their dependencies with Codex, Claude Code, or Grok Build.
- Finding verification: Run follow-up scripts to check exploitability, create proofs of concept, and draft reports for potential vulnerabilities.
- Custom prioritization: Apply your own severity criteria, give findings a consistent structure, and remove duplicates before reviewing results.
- Result exports: Download findings, reports, proofs of concept, and structured scan data together, with partial results clearly marked when a scan stops or fails.
The free, open-source engine uses the AGPL-3.0 license and runs on your own infrastructure with Docker Compose and a browser interface. Model access is separate: it accepts a Codex login or connections to OpenAI, Anthropic, DeepSeek, OpenRouter, or xAI. Self-hosting the orchestration doesn't make those external model services local.
Kritt also offers paid managed scans, where its security research team operates the workflow and delivers a written report of validated findings.
 Logotyper


